Free, open source
whistleblowing
software
OpenWhistle is free, open source whistleblower software: the self-hosted internal reporting channel that EU Directive 2019/1937 and Germany's HinSchG require.
Anonymity you can verify, not trust.
No IP address at any layer, report times as the day only, attachment metadata removed.
How to check it →Built for the reporting office.
7-day and 3-month deadlines, four-eyes deletion, audit log, roles and locations.
The admin guide →Free and under your control.
Your server, your data, no licence fee, no vendor.
Install it →From report to closed case
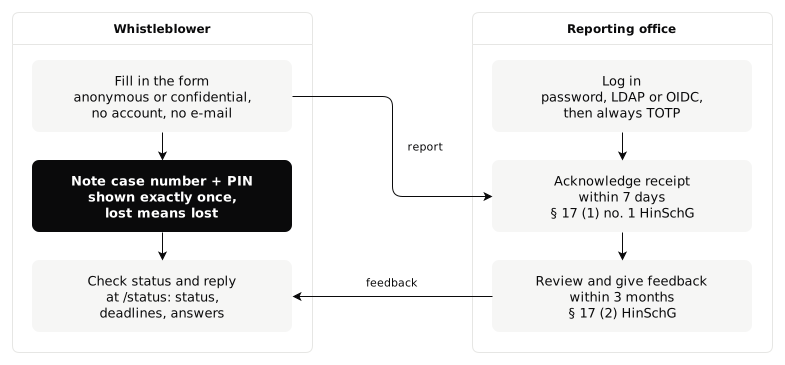
What each side gets
| Access | Case number and a UUID4 PIN, shown once. No account, no email address. |
| Mode | Anonymous, or confidential: name and contact encrypted, shown to the case handler only after an audited reason |
| Follow-up | Read replies and send messages at /status with case number and PIN |
| Case work | Statuses, assignment, internal notes, linked cases, PDF export |
| Alerts | Opt-in email and webhook digests and deadline reminders |
| Sign-in | Password, LDAP or OIDC, then always TOTP. Enrolment is mandatory. |
| Encryption | Each report has its own data key; the master key is never in the database |
| Languages | 5 languages: English, German, French, Spanish, Brazilian Portuguese |


Compliance by jurisdiction
EU Directive 2019/1937
Private employers with 50 or more workers, financial services firms at any size, and the public sector need an internal channel. Reports are acknowledged within 7 days and answered within 3 months.
Requirement by requirement →Germany: HinSchG
The Whistleblower Protection Act has applied since 2 July 2023. Running no internal channel can cost up to €20,000 (a summary, not legal advice).
Section by section →Further jurisdictions
The core follows ISO 37002; another law is a profile on top.
How the profiles work →Check it yourself
OpenWhistle has one maintainer and no external audit yet. Everything else you can check yourself: the code, the signed images, and the list of every request that leaves your server.
Try it, then run it yourself
The public demo signs you in with prefilled credentials and is wiped every 6 hours. Never enter a real report there.
Your own installation takes three commands and one edit of .env. The /setup wizard then creates the first account.
$ cd OpenWhistle && cp .env.example .env
# .env: COMPOSE_FILE, SECRET_KEY, DATABASE_URL, REDIS_URL
$ docker compose up -d
# Then open https://localhost/setup with the token from the app log